ISO 13485 is no longer just a standard. In the United States, it's the regulation.
For thirty years, FDA inspections ran against the Quality System Regulation and ISO 13485 was the voluntary international equivalent. That ended in February. The QMSR now incorporates ISO 13485:2016 by reference, which means the requirements you used to meet by choice are the ones an FDA investigator arrives holding. If your quality system was built to the old Part 820 and never fully reconciled with 13485, that gap is now a compliance gap.
Book a free 30-minute callThirty minutes to work out where your system actually stands against the new regulation, and what closing the distance would take.
What the QMSR actually changed
The shift is real but narrower than some of the consulting noise suggests. Four things are worth understanding before you spend money on anything.
Compliance is required. Certification still isn't.
The FDA requires you to meet the requirements of ISO 13485 as written into Part 820. It does not require you to hold a certificate from a registrar, and a certificate does not exempt you from FDA inspection. Certification is worth pursuing for market access and customer confidence, not because the FDA asks for it.
The regulation is locked to the 2016 edition.
The QMSR incorporates ISO 13485:2016 specifically. If ISO publishes a later edition, it does not automatically become US law — that would take fresh rulemaking. You are building against a fixed target, which is unusually comfortable ground in this business.
The FDA kept some requirements of its own.
The QMSR is not simply ISO 13485 with a federal cover page. Labeling and packaging controls, unique device identification, certain record and definition provisions, and the FDA's own expectations on complaint and servicing records all sit on top of the standard.
Build the quality system first, then the medical device layer
To be clear about something the market often muddles: ISO 13485 is a standalone standard. You do not need ISO 9001 certification first, and no registrar or notified body will ask for it. But the two standards share most of their foundations — document control, purchasing, competence, internal audit, management review, corrective action — and roughly three quarters of the work of building a 13485 system is building a sound quality system, full stop.
That's why my material is structured in two parts. The implementation course builds the quality system itself, clause by clause, with the procedures and forms written out and a completed example of each. The medical device add-on then covers everything ISO 13485 requires that ISO 9001 doesn't: the regulatory reporting obligation, risk management across the product lifecycle, the medical device file, design controls, validation driven by risk, sterile device requirements, and the infrastructure and personnel controls. It also maps the clause numbering, because ISO 13485:2016 kept the older structure — clauses 4 through 8, with management responsibility at 5 and product realization at 7 — rather than adopting the layout ISO 9001 now uses.
Work through the first part and you have a system that would satisfy an ISO 9001 auditor. Add the second and you have one built for the QMSR and a 13485 registrar. Nothing from the first part gets thrown away.
What ISO 13485 asks of you
Stripped of the language, the standard asks you to establish how a device gets designed, made and serviced safely, do it that way every time, keep records that prove it, and act on problems in the field. Where it parts company with ISO 9001 is in how much of that has to be written down, and in who you answer to when it goes wrong.
Where it goes beyond ISO 9001
- Regulatory obligation replaces customer satisfaction as the organizing idea
- ISO 9001 is built around meeting customer requirements and improving continually. ISO 13485 is built around meeting regulatory requirements and maintaining process effectiveness. That is not a small rewording. It changes what your management review discusses, what your objectives measure, and it adds an obligation to report to regulatory authorities that has no equivalent in ISO 9001.
- Risk management runs through the whole lifecycle, not just your planning
- Risk-based thinking in ISO 9001 largely shapes how you plan. In ISO 13485 risk drives specific decisions: which processes need validation, how far verification has to go, what design controls apply, and what post-market surveillance you owe. In practice this means working to ISO 14971 alongside the QMS, and being able to show the reasoning behind each decision rather than asserting that you considered risk.
- Documentation is heavier, and specific records are named
- You need a medical device file for each device or family, design and development records that trace requirement to verification, and retention periods tied to device lifetime rather than to whatever your document control procedure happens to say. An auditor will pick a device and follow it from design input through to a shipped unit. Any break in that chain is a finding.
- Sterile devices bring their own requirements
- If you sterilize, the process has to be validated and the validation kept current — not run once and filed. Contamination control, sterile barrier integrity, and validation of the packaging process itself all apply. Records for each sterilization batch have to be traceable to the devices in it.
- The building and the people in it become controlled
- ISO 13485 sets explicit expectations that infrastructure prevents mix-up and contamination: separated areas, controlled environmental conditions where the product needs them, and documented requirements for personnel health, cleanliness and clothing. For a shop coming from commercial or aerospace work, this is usually the most unfamiliar part of the standard.
Who you'd be working with
I'm Steve Kent. I've spent over forty years in quality management, most recently as a Quality Director, with roughly twenty of those years working on ISO 9001 and its derivatives — AS9100 in aerospace and ISO 13485 in medical devices.
I've built quality systems from nothing and rebuilt ones that had quietly stopped working. I've prepared companies for registrar audits and I've sat on the other side of the table during them, which matters more than it sounds: knowing what an auditor is looking for is a different thing from knowing what the clause says.
Falcon Quality is a one-person practice by choice. There's no account manager and no junior consultant doing the work under my name. If you engage me, you get me.
I'll also tell you plainly when something is outside what I do. I'm a quality systems specialist, not a regulatory affairs consultant — I can build you a QMS that satisfies ISO 13485 and the QMSR, and I'll tell you when you need a regulatory or notified-body specialist alongside me rather than pretending otherwise.
More about how I work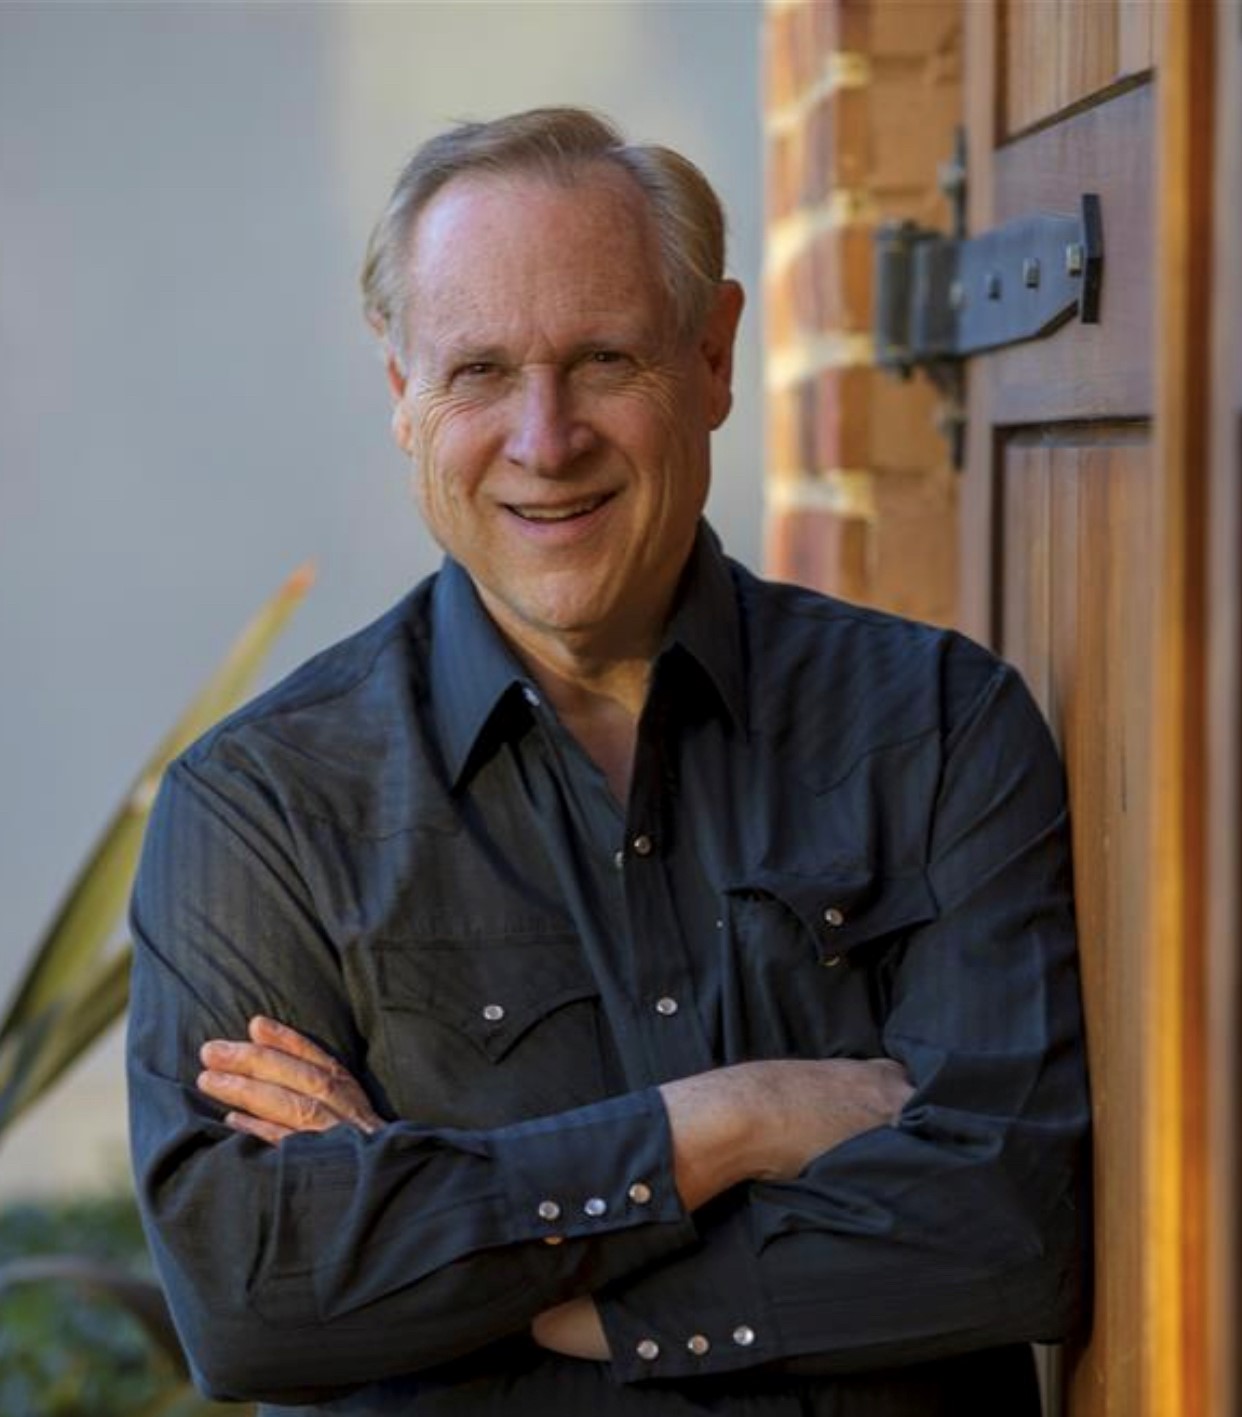
How the work goes
Four stages, the same shape as any QMS project, with more documentation at every step than an ISO 9001 build. How long it takes depends on how many devices you make, whether you design them, whether you sterilize, and how much of a system already exists. Anyone quoting you a fixed duration before seeing your operation is guessing.
-
Map what exists against what's required
A clause-by-clause review of your current system against ISO 13485 and the QMSR additions, including whatever was built to the old Part 820 and needs reconciling.
-
Build the system
Procedures, the medical device file structure, design controls where you design, risk management tied to ISO 14971, and the records to support all of it. Written for how your operation actually runs.
-
Run it and generate the evidence
Training, a full internal audit cycle, and management review conducted properly. Registrars and investigators both want proof the system has been operating, not just that the documents exist.
-
Audit or inspection readiness
Mock audit, preparation for Stage 1 and Stage 2 if you're certifying, FDA inspection readiness if you're not, and support closing whatever gets raised.
What it costs to do this with help
The two courses together are the self-directed path. For medical device work I'd advise adding consulting calls to them — more strongly than I would for ISO 9001. The parts of ISO 13485 with no ISO 9001 equivalent are exactly the parts where a course can only take you so far: which processes need validation and to what depth, how your design history file should be structured for the device you actually make, what your sterilization validation has to demonstrate, and where your risk file and your quality system have to line up. Those answers are specific to your device and your operation, and getting them wrong is expensive to unwind after an auditor finds it. The call is free either way.
Step one: the implementation course
Eight modules building the quality system clause by clause, with every procedure and form already written and a completed example of each. This is the three quarters of ISO 13485 that is simply sound quality management.
See what's coveredStep two: the medical device add-on
Everything ISO 13485 requires that ISO 9001 does not — regulatory reporting, lifecycle risk management, the medical device file, design controls, risk-based validation, sterile device requirements, infrastructure and personnel controls — plus the clause mapping between the two structures.
Ask me about the add-onConsulting calls — recommended
One-to-one time on the decisions a course can't make for you: validation strategy, design controls for your specific device, sterilization and risk file questions, audit preparation. Blocks of five calls for $600 or ten for $1,000. Most people doing 13485 work want these alongside the courses.
How the calls workBefore any of that, the free gap analysis will give you a reading on the ISO 9001 foundation — the part both standards share. It won't cover design controls, sterilization or the medical device file, so treat it as a temperature check rather than a 13485 audit. Start the assessment
Common questions
- Do I have to be certified to ISO 13485 to sell in the United States?
- No. You have to comply with the QMSR, which incorporates ISO 13485:2016 by reference, but the FDA does not require a certificate and holding one does not exempt you from inspection. Certification matters for EU market access, for customers and distributors who require it, and for MDSAP participation. It is a commercial decision rather than a federal requirement.
- Is ISO 13485 certification enough for the EU?
- No, though it's a necessary piece. The Medical Device Regulation and the In Vitro Diagnostic Regulation both impose obligations beyond the standard — clinical evaluation, technical documentation, post-market surveillance and vigilance reporting among them — and conformity assessment runs through a notified body. Certification demonstrates the quality system element. It does not carry the rest.
- Should I wait for a new edition of ISO 13485?
- No. ISO reviewed the standard in 2025 and confirmed the 2016 edition as current with no revision underway, partly to keep it stable now that the FDA has written it into regulation. The next systematic review falls around 2030. Unlike ISO 9001, where the sixth edition just published, there's nothing coming that would change what you build.
- Do we need ISO 9001 certification before we can get ISO 13485?
- No. ISO 13485 is a standalone standard and you can certify to it without ever holding ISO 9001. No registrar or notified body will ask you for one as a prerequisite. What is true is that most of the work overlaps, which is why building the quality system properly comes first in practice — not as a certification step, but because the medical device requirements sit on top of foundations that have to exist before they mean anything.
- We're ISO 9001 certified. How much of that carries over?
- A useful amount, though less neatly than you might expect. Your document control, purchasing, competence, internal audit, management review and corrective action processes are a genuine foundation rather than a false start. The catch is the numbering: ISO 13485:2016 kept the older clause structure, so it runs to clause 8 with management responsibility at 5 and product realization at 7, and never adopted the layout ISO 9001 has used since 2015. Your processes transfer; your clause map doesn't. On top of that you'll add regulatory reporting, risk management to ISO 14971 across the lifecycle, the medical device file, design controls if you design, risk-based validation, and the infrastructure and personnel requirements.
- We're a contract manufacturer. Does the whole standard apply to us?
- Not all of it. If your customer holds the design and you build to their specification, design and development may be a legitimate exclusion — the standard permits exclusions where a requirement doesn't apply to your activities, provided you justify them in writing. What catches contract manufacturers out is the opposite direction: traceability, process validation and contamination control often apply more heavily than expected, and your customer's regulatory obligations flow down to you through the contract whether or not the clause names you.
- What does certification cost?
- The registrar's fee is separate from anything I charge and is higher than for ISO 9001, since audits take longer and the auditors are more specialized. Budget more if you sterilize or design. Get quotes from two or three accredited registrars early, and ask specifically whether they're accredited for your device class and whether they can perform an MDSAP audit if you're considering multiple markets.
- Do you work remotely?
- Yes, and most of this work is remote regardless of location. I'm based in Danville, California, so on-site work is straightforward in the Bay Area and possible elsewhere. Some parts of a medical device build — walking your production areas, reviewing contamination controls, a mock audit — genuinely benefit from being in the room, and I'll say so when that's the case.
Find out what the QMSR means for your system.
Thirty minutes, no charge, no obligation. Tell me what you make and what state your quality system is in, and I'll tell you what the work actually involves — including whether you need to hire anyone at all.
Find out where you stand before you spend anything.
Sixty-seven questions across every clause of ISO 9001, scored by section. Set aside 30 to 45 minutes. Free, and your answers save as you go.
ISO 9001, AS9100 and ISO 13485 consulting and courses for small and medium manufacturers. A one-person practice — you work with me, not an account manager.
- Phone
- (925) 557-8570
- [email protected]
- Office
- 499 Highland Dr
Danville, CA 94526
Falcon Quality is an independent consultancy. It is not a certification body, a registrar or an accreditation organization, and it does not issue certificates. ISO 9001, AS9100 and ISO 13485 are the property of their respective standards organizations.